About WordPress MCP Server
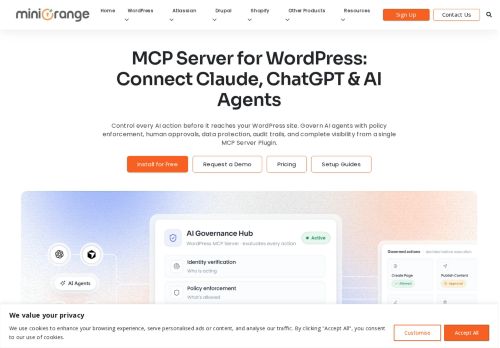
MCP Server for WordPress provides AI policy enforcement and request evaluation for WordPress sites via an MCP Server plugin. It authenticates AI agents with unique non-human identities, enforces role-based permissions, and evaluates each request through multi-stage policy checks.
Data rules and DLP redaction mask sensitive information before it reaches models, while prompt-injection detection and behavioral anomaly monitoring reduce operational risk.
The plugin governs REST API and WP-CLI actions, discovers WordPress and WooCommerce abilities, and applies per-agent limits, quotas, and multisite policies.
Human-in-the-loop workflows route high-risk actions for approval and dry-run simulation lets teams test policies against real requests without affecting production. Immutable audit trails, scheduled access reviews, and agent reputation scoring record activity and support compliance reporting.
Compatible with MCP-aware AI clients, the MCP Server centralizes visibility and control over AI-driven interactions with WordPress.
Key Features
Use Cases
Who is it for?
Data rules and DLP redaction mask sensitive information before it reaches models, while prompt-injection detection and behavioral anomaly monitoring reduce operational risk.
The plugin governs REST API and WP-CLI actions, discovers WordPress and WooCommerce abilities, and applies per-agent limits, quotas, and multisite policies.
Human-in-the-loop workflows route high-risk actions for approval and dry-run simulation lets teams test policies against real requests without affecting production. Immutable audit trails, scheduled access reviews, and agent reputation scoring record activity and support compliance reporting.
Compatible with MCP-aware AI clients, the MCP Server centralizes visibility and control over AI-driven interactions with WordPress.
Key Features
- Multi-stage AI policy enforcement and request evaluation via MCP Server plugin
- Authentication of AI agents with unique non-human identities and role-based permissions
- Data rules with DLP redaction, prompt-injection detection, and behavioral anomaly monitoring
- Governance of REST API and WP-CLI actions with discovery of WordPress/WooCommerce abilities and per-agent limits, quotas, and multisite policies
- Human-in-the-loop workflows, dry-run policy simulation, immutable audit trails, scheduled access reviews, and agent reputation scoring
Use Cases
- Enforce enterprise-grade AI governance for WordPress chatbots and content generators by authenticating non-human agents, applying role-based permissions, detecting prompt-injection attacks, and routing risky responses to human-in-the-loop approvals with immutable audits for regulatory compliance
- Protect customer and business data in AI workflows on WordPress by applying DLP redaction and request evaluation to redact PII and secrets before output, while monitoring agent behavior and enforcing quotas to prevent data exfiltration
- Centralize control of third-party AI integrations on your WordPress site by authenticating agents, setting per-agent rate limits and behavioral policies, maintaining immutable audit trails for incident investigations, and automatically blocking or quarantining suspicious agents
Who is it for?
- Wordpress site administrators
- Woocommerce/store managers
- Devops/platform engineers
- Security/infosec teams
- Compliance and legal officers
- Ai/ml engineers and integrators
- Plugin and extension developers
- It auditors and risk managers
- Site owners and product managers
No review yet!
More Developer tools AI Tools
Explore other developer tools tools with user ratings, pricing details, and in-depth descriptions. Updated regularly by our editorial team.