About ARTEX
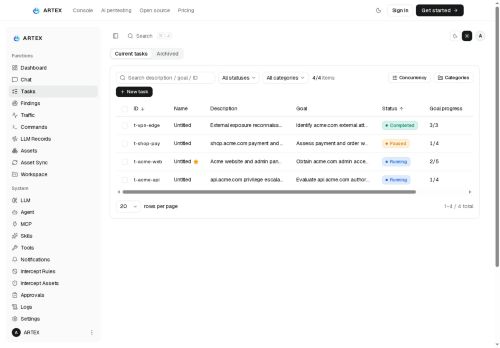
ARTEX is an autonomous pentesting console that coordinates AI-driven security agents to plan and execute automated security assessments.
It centralizes engagement planning, task orchestration, and findings review in a single workspace.
Built-in tools track tasks, capture traffic and commands, record LLM activity, and log results for audit and analysis.
Asset synchronization and approval workflows help manage test scope and maintain controlled execution.
Dashboard, chat, and reporting features provide real-time monitoring of progress and remediation status.
The project is open source and offers self-hosting and integration options, with a GitHub mirror for code access.
Key Features
Use Cases
Who is it for?
It centralizes engagement planning, task orchestration, and findings review in a single workspace.
Built-in tools track tasks, capture traffic and commands, record LLM activity, and log results for audit and analysis.
Asset synchronization and approval workflows help manage test scope and maintain controlled execution.
Dashboard, chat, and reporting features provide real-time monitoring of progress and remediation status.
The project is open source and offers self-hosting and integration options, with a GitHub mirror for code access.
Key Features
- Autonomous pentesting console coordinating AI-driven security agents to plan and execute automated security assessments
- Centralized workspace for engagement planning, task orchestration, findings review, and real-time dashboard/chat/reporting
- Built-in tools for task tracking, network traffic and command capture, LLM activity recording, and result logging for audit and analysis
- Asset synchronization and approval workflows to manage test scope and enforce controlled execution
- Open-source project with self-hosting and integration options and a GitHub mirror for code access
Use Cases
- Run continuous, self-hosted autonomous pentesting campaigns with ARTEX to coordinate AI-driven security agents, centralize engagement planning and capture traffic and command artifacts for audit-ready, repeatable assessments
- Streamline enterprise security assessments and compliance workflows by syncing assets from your inventory, orchestrating automated tests with approval gating in ARTEX, and generating consolidated reports with LLM activity logging for traceability
- Accelerate red-team/SOC collaboration and analyst training by using ARTEX to plan automated attack scenarios, log agent decisions and captured evidence for forensic review, and produce actionable remediation playbooks for developers and ops teams
Who is it for?
- Penetration testers
- Red team operators
- Security engineers
- Vulnerability assessment teams
- Vulnerability management teams
- Devsecops engineers
- Security operations (soc/secops) teams
- Security consultants
- It/security managers and directors
- Compliance and audit teams
No review yet!
More Security and Privacy AI Tools
Explore other security and privacy tools with user ratings, pricing details, and in-depth descriptions. Updated regularly by our editorial team.