About TryBoxi
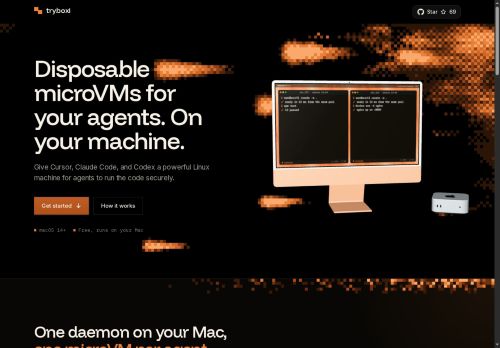
tryboxi provides disposable microVMs on your machine to run agents in isolated sandboxes.
A local daemon, sandboxd, manages one microVM per agent and exposes an HTTP API over a unix socket for direct control.
MicroVMs are provisioned rapidly (milliseconds to sub-second) and can have a repository synced into the sandbox at startup.
Outbound access is routed through an allowlist egress proxy and secrets are not placed inside the VM.
Integrations use the MCP protocol and agent runtimes such as Cursor, Claude Code, and Codex can connect; SDKs and CLI tools are available for Python, Go, and HTTP/curl.
Installation builds from source and requires Go and an initial image build; after install the daemon runs without elevated privileges.
The architecture leverages macOS virtualization frameworks and supports programmatic control via the sandboxd API.
Key Features
Use Cases
Who is it for?
A local daemon, sandboxd, manages one microVM per agent and exposes an HTTP API over a unix socket for direct control.
MicroVMs are provisioned rapidly (milliseconds to sub-second) and can have a repository synced into the sandbox at startup.
Outbound access is routed through an allowlist egress proxy and secrets are not placed inside the VM.
Integrations use the MCP protocol and agent runtimes such as Cursor, Claude Code, and Codex can connect; SDKs and CLI tools are available for Python, Go, and HTTP/curl.
Installation builds from source and requires Go and an initial image build; after install the daemon runs without elevated privileges.
The architecture leverages macOS virtualization frameworks and supports programmatic control via the sandboxd API.
Key Features
- Disposable microVMs for running agents in isolated sandboxes
- Local daemon (sandboxd) that manages one microVM per agent and exposes an HTTP API over a unix socket for direct control
- Rapid microVM provisioning (milliseconds to sub-second) with optional repository sync into the sandbox at startup
- Outbound traffic routed through an allowlist egress proxy and secrets are not placed inside the VM
- Integrations via the MCP protocol with support for agent runtimes (Cursor, Claude Code, Codex) and SDKs/CLI for Python, Go, and HTTP/curl
Use Cases
- Run automated security and CI tests for pull requests in ephemeral microVMs using Tryboxi's sandboxd HTTP API to rapidly provision isolated, unprivileged sandboxes with repository sync, egress allowlisting and no in‑VM secrets—letting you safely execute untrusted code and catch regressions without risking host resources
- Develop and validate AI agents and automation workflows locally by launching disposable agent sandboxes via Tryboxi's Python/Go SDKs and MCP integrations, controlling outbound access with the egress allowlist proxy and keeping credentials off‑VM for secure, repeatable agent execution
- Provide reproducible developer sandboxes for code review, debugging and pre‑merge checks by spinning up microVMs from a repo snapshot with Tryboxi's programmatic API—enabling fast provisioning, isolated debugging, CI/CD integration and strict network controls via an unprivileged sandbox daemon
Who is it for?
- Ai/ml engineers developing and testing agent-based systems
- Software engineers integrating agent runtimes (cursor, claude code, codex)
- Security engineers needing isolated execution for untrusted code
- Devops/sres managing local microvms and ci/cd workflows
- Qa engineers testing agent behavior and reproducibility
- Platform/tooling engineers building sdks, clis, and integrations (python/go/http)
- Research scientists experimenting with agent behavior and environments
- Macos developers leveraging native virtualization for sandboxing
No review yet!
More AI Agents AI Tools
Explore other ai agents tools with user ratings, pricing details, and in-depth descriptions. Updated regularly by our editorial team.